



The mobile app development process has a reliable blind spot: the operational work that lives outside sprint plans. Signing certificates, IAM handoffs, store compliance, and release governance don’t appear on roadmaps but they determine whether a feature-complete app ships on time or stalls in the last mile.
Key Points
- Platform commitment, MVP scope, and team topology decisions must be made before development begins, not discovered mid-sprint.
- Release readiness (signing access, distribution paths, store assets, privacy disclosures) is a common source of late-stage delay for enterprise mobile launches.
- A decision checkpoint process gives every decision an owner and every exit an explicit criterion, so scope creep and dependency gaps surface when they’re still cheap to fix.
- Post-launch operations aren’t optional: OS updates and app store policy shifts will arrive whether or not you’ve budgeted for them.
You can run a disciplined mobile app development process, complete with sprint cadence, a roadmap, and a fully staffed team, and still miss your launch date. According to Bitrise’s Mobile DevOps Assessment (MODAS), a benchmark built from self-reported data across more than 1,600 mobile teams, 44% of companies say their release approval process is mostly or entirely manual, and only 22% can complete an internal release in under an hour. Individually, those slowdowns are usually resolved in hours or days. The problem is that they compound: a provisioning renewal here, an MDM distribution hiccup there, an IAM dependency that surfaces in week eight. None of them is a crisis on its own, but a process with no owner for any of them accumulates delay the same way technical debt accumulates, quietly, until it’s all due at once near launch.
For engineering leaders, the challenge isn’t simply developing mobile apps. It’s ensuring the entire mobile app development lifecycle moves from concept to production without hidden bottlenecks. A more reliable approach is to treat the app development process as a series of decision checkpoints, each with clear ownership, measurable exit criteria, and explicit risk management objectives. That framework surfaces constraints early, controls scope, and creates a repeatable path to app launch.
Why Decision Checkpoints, Not Steps
A step implies a straight line: finish it, move to the next one. A checkpoint implies evaluation: someone looks at the evidence, makes the call, and owns the outcome.
Unlike a stricter gate model, a checkpoint isn’t inherently binary. A team can clear a checkpoint outright, clear it conditionally with one item flagged for remediation, defer a piece of scope to a later release, or send a decision, such as an architecture choice or a platform commitment, back for another look before moving on. That flexibility matters for mobile specifically: the ecosystem changes constantly, and a framework that only allows pass or fail doesn’t match how these decisions actually get made in practice. The structure here borrows the underlying discipline of stage-gate style reviews, an approach widely used in product development to place explicit decision authority at set points in a project, but adapts it into something less rigid and better suited to a practical operating framework than to formal program governance.
To illustrate: an enterprise field app using OIDC, conditional access, and MDM distribution can look feature-complete while still being unshippable. If the IAM team owns token lifetimes, the MDM team owns distribution, and a single engineer knows the Apple account, you’ve built a slow delivery path with no owner for the last mile. This is exactly the kind of cross-team dependency that stalls otherwise well-run projects. Teams that bring in a dedicated release engineering partner, which is a problem BairesDev works through with clients regularly, usually solve it the same way: name one accountable owner across IAM, MDM, and signing before the first sprint starts, instead of discovering the gap in week eight.
Checkpoint 1: Platform Commitment
You can have a clean roadmap and a staffed team, then discover your “minor” platform choice forces native-only work when you’re supposed to be stabilizing.
One leadership rule keeps this crisp: let required device capability set the floor, and let staffing and maintenance set the ceiling.
This is ultimately a mobile app development strategy decision rather than a purely technical choice. The platform you select affects mobile app development costs, staffing requirements, testing complexity, and long-term ownership.
If the product depends on deep OS features, such as background execution, hardware integrations, or biometric flows, native app development buys down risk. Those requirements should be documented as part of the application’s core features before the development team commits to a specific technology stack and programming languages. Native development means Swift and Kotlin; cross-platform means Dart or JavaScript, a choice that affects hiring, code review standards, and long-term ownership.
If your app is mostly standard screens and workflows where iteration speed and feature parity matter more than edge capability, cross-platform app development often reduces long-term cost.
If distribution friction and release speed dominate and you don’t need reliable native behaviors, a progressive web app built on web technologies can be the lowest-governance path. The trade-offs here are narrower than they used to be but haven’t disappeared. Since iOS 16.4 (released in 2023), home-screen-installed PWAs on iOS can receive web push notifications, so “no push on iOS” is no longer accurate as a blanket statement. Background sync, however, remains genuinely limited on iOS compared to native apps. Governance is also a live variable, not a settled fact: in February 2024, Apple briefly moved to remove home-screen web app functionality entirely for EU users as part of Digital Markets Act compliance, then reversed the decision about two weeks later following developer and regulator pushback, restoring the feature with iOS 17.4. The episode is a useful reminder that PWA capability on iOS has changed twice in two years and can change again; teams betting on the PWA path should treat platform-level dependency as something to monitor, not assume.
Note that PWAs and hybrid apps aren’t the same thing: hybrid apps wrap web content inside a native shell and distribute through app stores, which reintroduces the signing, compliance, and review overhead you were trying to avoid.
| Approach | Best fit | Trade-off |
| Native mobile apps (iOS / Android) | Deep OS capability required | Separate codebases; higher staffing cost |
| Cross-platform app (React Native, Flutter) | Standard UI, parity matters | Some native modules still needed |
| Progressive web app | Speed to distribute, low governance | Background behavior still limited on iOS; push notification support and platform rules have shifted more than once |
Exit criteria:
- Your team lists the non-negotiable device/OS capabilities, and what breaks if any one is degraded.
- You’ve defined 2–3 performance targets you’ll actually enforce: cold start, offline sync time, crash-free session rate.
- You’ve documented the 18–24-month staffing plan: one team vs. two, native-module ownership if cross-platform, partner vs. in-house boundaries.
- You’ve recorded explicit “won’t do in v1” constraints that prevent platform-driven scope creep. An example is “no background location in v1” or “no MDM distribution in v1.”
Checkpoint 2: MVP Contract and Scope Control
A VP asks for “just one more” capability in v1, and QA’s workload doubles. That one addition affects auth, offline behavior, and analytics, and drags out your timeline. If you can’t price that request in days and device coverage, you’ll pay for it in surprises.
Instead of writing “offline mode” as a requirement, write something like this: “Create a work order offline, queue it, sync within X minutes on reconnect, no data loss across app restarts, and a user-visible conflict rule.” That single sentence forces decisions about local storage, background behavior, retry semantics, telemetry, and supportability, exactly what you want while you can still change the plan.
The same discipline scales across complexity levels:
- Simple journey: “User opts into push notifications during onboarding. Decline doesn’t block onboarding. Re-prompt once, at day 7, with a stated reason.” This is a one-screen decision, but it still forces a call on permission timing, re-prompt frequency, and what “declined” means for downstream messaging.
- Medium journey: “Guest checkout completes with one saved payment method, order confirmation renders within 5 seconds, and a network retry never produces a duplicate charge.” This pulls in payment tokenization, idempotency keys, and a UI state for “processing” versus “failed.”
- Complex journey: the work-order example above, where offline storage, sync, conflict handling, and telemetry all have to be specified before a single screen gets built.
Before a single app idea becomes a sprint ticket, define your minimum viable product as journeys with measurable outcomes like these. For most mobile app projects, the goal isn’t to maximize functionality. What actually earns a place in v1 should come from evidence, not opinion: interviews with the people who’ll use the app, usage data pulled from whatever system (paper, spreadsheet, legacy app) it’s replacing, and a look at what comparable products in the same category ship as table stakes. That evidence is what the checkpoint contract locks in, and everything else stays out.
Scope control only works if you make change-cost visible, and that means the policy needs teeth, not just a general rule. Set it up like this:
- Veto power sits jointly with Engineering and Product leads. If they disagree, it escalates to the checkpoint owner (typically the program or delivery lead) rather than getting resolved in a hallway conversation.
- New scope requires either a date move or a same-sprint swap of “comparable test surface area,” defined concretely as: a journey with a similar number of device/OS combinations and a similar number of distinct test paths (happy path plus edge cases) to the one being removed. If the swap isn’t roughly equivalent on both counts, it’s not a swap, it’s added scope, and the date moves.
Exit criteria:
- You have 3–7 named v1 journeys with acceptance criteria.
- You have a written “won’t ship in v1” list covering device features, roles, regions, and distribution method.
- A change-control policy names who holds veto power and defines “comparable test surface area” in terms both Engineering and Product can apply without re-litigating it every sprint.
Checkpoint 3: Team Topology and Partner Model
Let’s say one team finishes screens, another owns OIDC claims, and a third holds the signing keys. If that’s your setup, don’t be surprised when every sprint ends at 90% done and 0% in production.
Ownership boundaries usually influence delivery speed more than organizational charts. A mobile app team structure can look fully staffed and still lose weeks to IAM waiting on a claim change, or security waiting to approve an analytics SDK. In mobile, those interfaces determine whether your sprint cadence is actually working.
Whether you’re running nearshore mobile app development or a fully in-house team matters less than whether the people building the app can complete a vertical slice. Nearshore delivery has a specific advantage here: teams working in overlapping time zones can get same-day sign-off on an IAM claim or pair through a signing issue live, instead of waiting a day for an answer across a 10-plus hour gap. If your pod owns UI but can’t clear access fast, you’ve built a dependency maze, and delivery gets stuck inside it.
Exit criteria:
- You’ve named owners for the interfaces that typically block mobile: IAM/auth, backend contracts, security/privacy approvals, and release (Apple/Google accounts, TestFlight/Play tracks).
- One lead has merge authority and parity responsibility across iOS/Android, or your shared stack, so platform drift doesn’t become a late surprise.
- Your partner model defines what “done” means operationally: a story isn’t done until it’s integrated and instrumented in CI through to internal distribution.
Checkpoint 4: CI/CD and Release Governance
On mobile, compiling doesn’t mean you’re done. The team can finish a sprint’s worth of features and still lose a week because the only person with App Store Connect access is on PTO.
Release work is a DevOps capability, and one of the most overlooked phases of the mobile app development lifecycle. The Bitrise MODAS data referenced earlier bears this out at scale: 44% of teams run release approval that’s mostly or entirely manual, and the same benchmark found testing is barely better off, with only 9% of teams reporting a fully automated testing process. “Release readiness” is a real, measured gap across the industry, not an edge case.
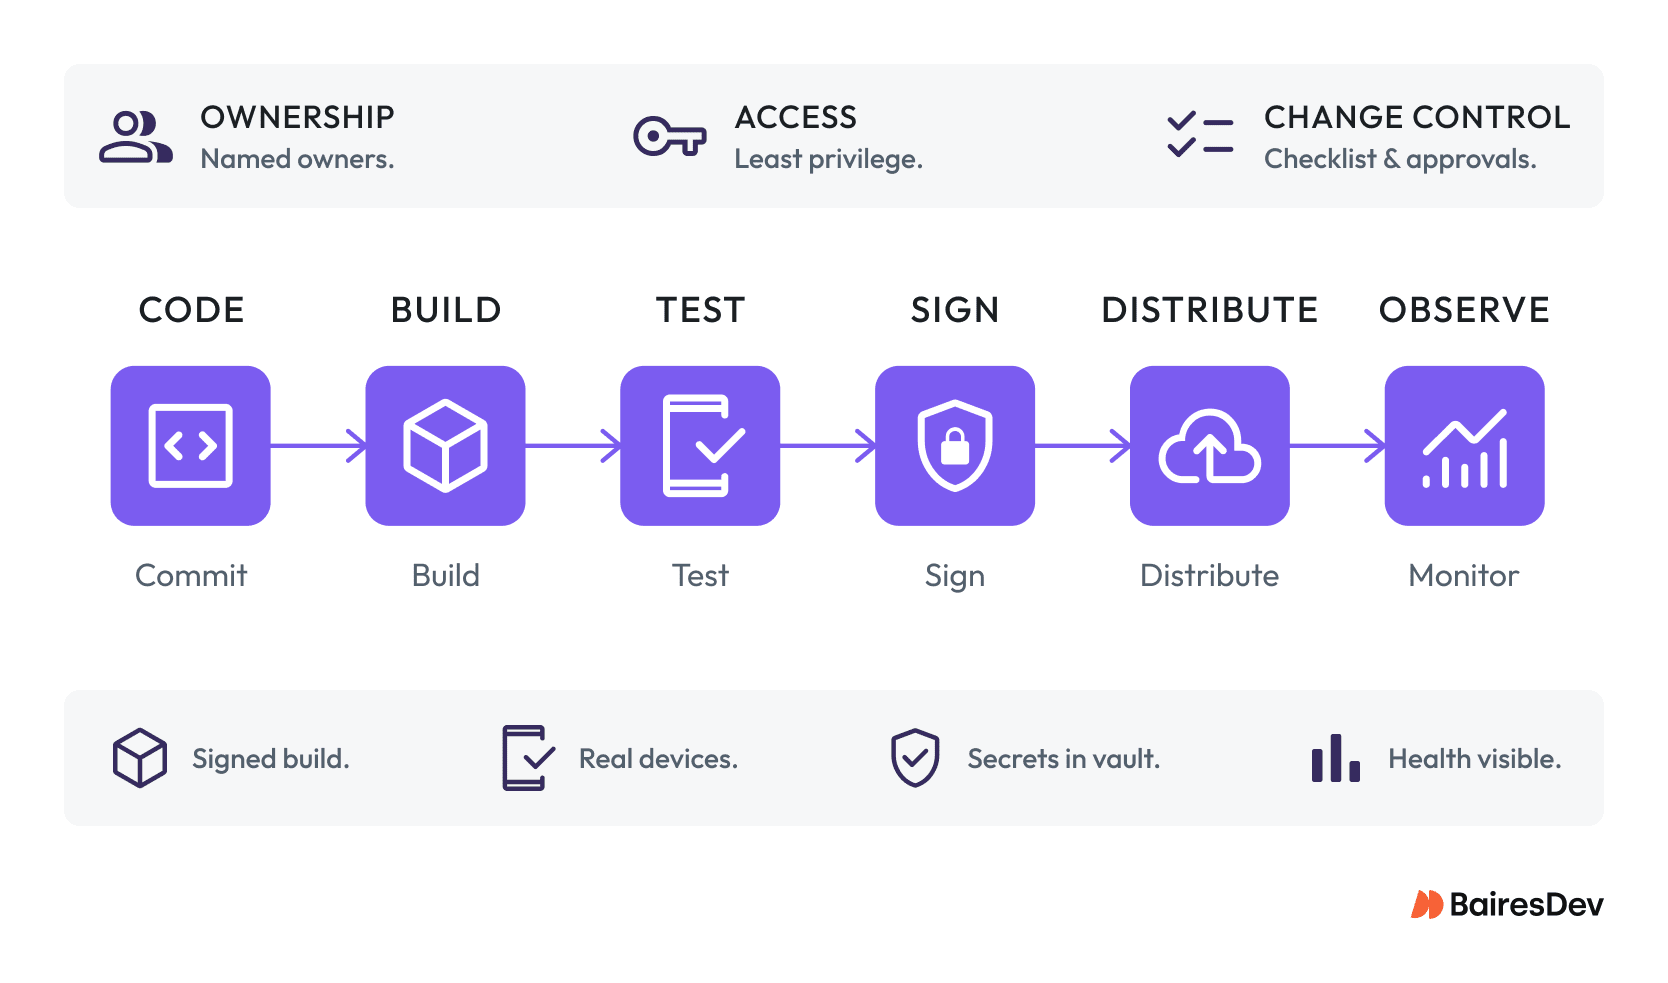
A ritualized, manual release creates single points of failure. Mobile punishes this more than web: every build artifact, whether it originates in Xcode, Android Studio, or a unified CI layer, must be correctly signed before anyone can validate it, including the stakeholders who’ll veto you in UAT. A broken signing setup doesn’t just delay your release; it blocks everyone who needs to validate the build before you can ship.
In practice, this means naming actual tooling rather than treating “release automation” as an abstraction. A common stack: Fastlane match for certificate and provisioning profile management, a secrets vault such as HashiCorp Vault or AWS Secrets Manager for API keys and signing credentials, and a CI platform with solid iOS signing support (Bitrise, GitHub Actions with macOS runners, or CircleCI are common choices) to run the pipeline end to end. None of this is exotic. It’s the baseline enterprise readers should expect a mobile release pipeline to include.
Exit criteria:
- CI produces an iOS/Android artifact on every merge to main and publishes it to the right channel (TestFlight, Play Internal Testing, or enterprise MDM) without manual intervention.
- Apple/Google accounts and provisioning have at least two named admins, audited access, and a documented rotation/renewal owner.
- Your cadence includes a standing release cut (even when you don’t submit every time) so you continuously exercise versioning, signing, and distribution paths.
- “Done” includes release hygiene: correct build numbers, release notes stubs, and environment config, so nothing is missing during a code freeze.
Checkpoint 5: Testing and Device Coverage Policy
Tier your coverage intentionally. Tier 1 covers the devices and OS versions used by your highest-priority users, such as field teams or highest-revenue segments. Run the critical regression suite against those real devices in CI so device-specific failures are caught before they reach a human tester.
Tier 2 covers the broader device and OS matrix. Use emulators and simulators for fast, repeatable automated tests, then use a cloud device farm such as BrowserStack or Firebase Test Lab for representative real-device coverage across less-common configurations. Both platforms support automated testing on hosted devices, making it practical to expand coverage without maintaining a large physical device lab.
Automate the repeatable paths where possible, but don’t try to automate every mobile test. Permissions behavior, app lifecycle and backgrounding, accessibility, network transitions, and device-specific interactions still need targeted manual validation. Unsupported device and OS versions should be named explicitly so support teams aren’t renegotiating scope after launch.
Whenever possible, representative potential users should participate in testing. Internal stakeholders rarely behave exactly like the target audience under real-world conditions.
Accessibility should be part of this policy as well. Teams should validate critical workflows against current Web Content Accessibility Guidelines (WCAG) requirements and platform accessibility standards. Accessibility testing can also expose broader quality issues because it forces teams to exercise workflows through different interaction patterns rather than relying only on the standard happy path.
Mobile app testing checklist, exit criteria:
- You’ve set tiered device/OS targets.
- You’ve automated sprint-blocking regression paths (auth, core journeys, offline/sync smoke tests) in CI, running against a cloud device farm rather than a fixed set of physical devices.
- You’ve reserved manual time for what automation won’t catch early: permissions behavior, app lifecycle and backgrounding, accessibility, and network chaos.
Checkpoint 6: App Store and Play Compliance
Submission ends with enforcement, not approval. In 2024, Apple reviewed 7.77 million app submissions and rejected 1.93 million with performance the top reason, accounting for over 1.2 million of those rejections, according to Apple’s own Transparency Report. Google blocked 1.75 million apps from the Play Store in 2025 for policy violations. Planning for at least one rework loop isn’t pessimism, it’s just being realistic.
Run the app store submission process as a first-class workstream from the start of the project, not a final-week task. Requirements often differ between the Apple App Store and Google Play Store, particularly around permissions, privacy disclosures, in-app purchases, subscriptions, and data collection practices.
You can pass UAT and still get blocked when your privacy disclosures don’t match what analytics or crash SDKs actually collect. Keep a running Jira ticket set and documentation packet for screenshots, support URLs, privacy disclosures, and reviewer notes.
Two compliance shifts in particular now catch teams off guard. Since May 2024, apps that use Apple’s listed required-reason APIs must declare the approved reasons for that usage in a PrivacyInfo.xcprivacy privacy manifest, and certain commonly used third-party SDKs are also subject to privacy-manifest requirements.
Apple has also introduced additional requirements around apps that send personal data to third-party AI providers. Because Apple’s requirements and guideline numbering can change, teams should verify the current App Store Review Guidelines and privacy requirements at submission time rather than treating a specific subsection number as permanent.
Exit criteria:
- Store listing assets, screenshots, privacy labels, support URLs, and reviewer notes are drafted before UAT begins.
- Analytics, crash reporting, permissions, and data collection are mapped to privacy disclosures.
- A release owner tracks Apple/Google review status, rejection reasons, remediation owners, and resubmission timelines.
- The team has planned at least one review/rework loop into the launch schedule.
Checkpoint 7: Post-Launch Operations and Ownership
Many organizations treat app launch as the finish line. For enterprise mobile app development, it’s closer to the beginning.
Operating systems update on schedules your roadmap didn’t account for. App store guidelines shift. Third-party dependencies introduce vulnerabilities. Device manufacturers release new hardware that breaks layouts you thought were stable. The most expensive maintenance strategy is assuming maintenance won’t be necessary.
What distinguishes successful mobile applications from ones that quietly accumulate technical debt isn’t the quality of the initial launch, it’s whether the organization defined operational ownership before the first build shipped. Without it, every OS update becomes a negotiation, every security patch a fire drill, and every compliance change a surprise.
Operational ownership should cover OS compatibility and security updates, dependency management, crash analysis, app performance monitoring, user feedback review, accessibility improvements, and compliance updates. That list doesn’t require a large team. It requires a named team with a clear escalation path and defined service-level objectives.
Exit criteria:
- A named owner is accountable for production support before the app ships.
- Incident escalation paths, SLOs, and on-call responsibilities are documented, not assumed.
- A process exists for collecting and prioritizing user feedback, including bug fixes and accessibility issues. Users control notification preferences, permissions, and data-sharing settings, and OS updates frequently change how those controls behave, making this a recurring operational concern rather than a one-time configuration.
- The team has a defined approach for evaluating OS updates and app store policy changes before they become blocking.
- Future feature enhancement decisions have a named approver and a lightweight prioritization process.
The Last Mile Is Where Mobile Launches Succeed or Fail
Enterprise mobile launches can stall even when feature development is on schedule. They often run into problems outside sprint plans: signing access, distribution paths, store assets, privacy disclosures, and the inability to get builds onto real devices before UAT. Every one of those failure modes has a checkpoint that catches it early, or doesn’t.
The checkpoint model forces the right conversation at the right time. Platform commitment before you’ve built features that depend on it. Scope control before QA inherits an expanding surface area. Release governance before a single engineer becomes a single point of failure. Post-launch ownership before the first OS update arrives unannounced.
Organizations that consistently ship mobile apps on schedule don’t treat release readiness, app testing, compliance, and post-launch operations as separate concerns. They treat them as part of the same development process: planned, owned, and governed from day one.
| Checkpoint | Key decision | Primary risk if skipped |
| 1. Platform | Native, cross-platform, or PWA | Late re-architecture when OS features are needed |
| 2. MVP Contract | Journey definitions and scope control | Unconstrained scope creep through hardening |
| 3. Team Topology | Ownership of blocking interfaces | Sprint work that’s always “almost done” |
| 4. CI/CD | Signed artifact pipeline and release governance | Manual heroics, UAT blocked by signing failures |
| 5. Testing | Tiered device/OS coverage policy | UAT failures on unsupported configurations |
| 6. Store Compliance | Privacy disclosures, assets, release owner | Post-UAT rejection and rework loops |
| 7. Post-Launch | Operational ownership and escalation model | Reactive maintenance, accumulating technical debt |


